Imagine a Nigerian supplier receives a message that appears to come from your company's accounts department, requesting payment to a different bank account. The visible sender reads billing@example.com, but your business never sent it. This type of impersonation is one reason domain-level email authentication matters.
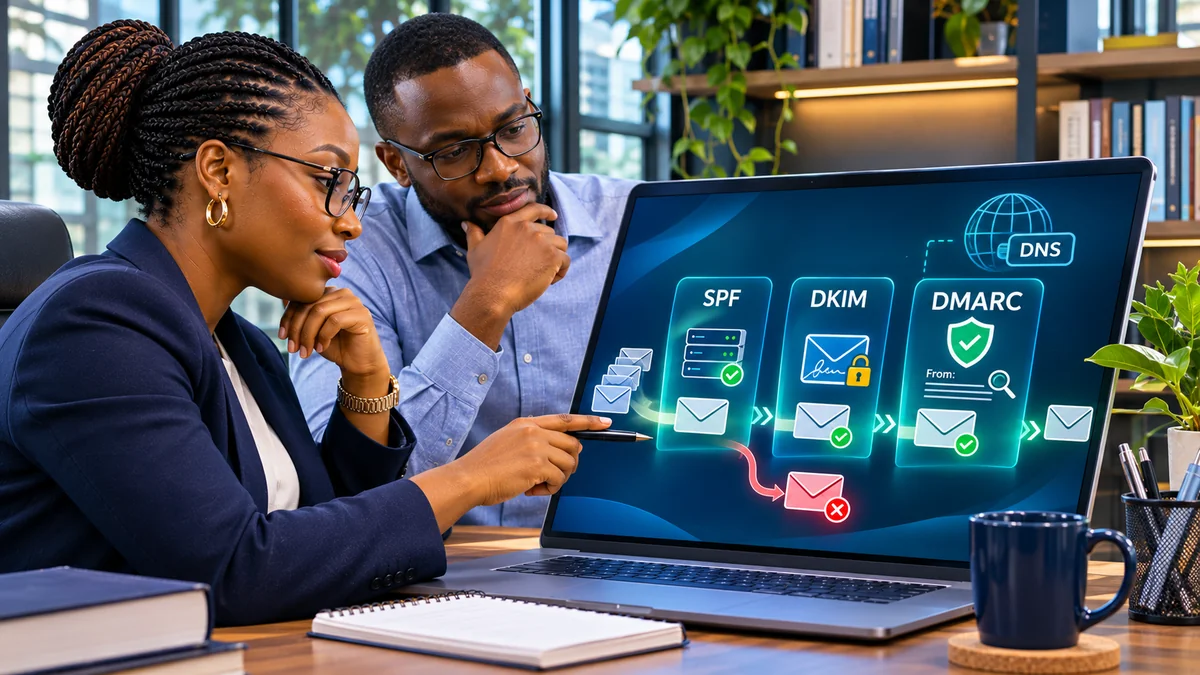
SPF, DKIM and DMARC are complementary standards that help receiving mail systems determine whether a message was authorised to use a domain and what to do when authentication fails. SPF checks authorised sending infrastructure, DKIM verifies a cryptographic email signature, and DMARC connects those results to the domain that recipients see in the From address. Together they reduce straightforward domain spoofing and can improve a legitimate sender's ability to meet mailbox-provider requirements—but they cannot guarantee inbox placement or prevent every phishing attack.
This practical SPF DKIM DMARC setup guide is intended for small businesses, publishers, online stores and service providers using domain-branded email. It includes safe example DNS records, a rollout checklist and real troubleshooting steps. All sample domains are illustrative; do not copy provider records without confirming your own sending services. Research verified: 2 November 2026.
1. SPF, DKIM and DMARC: The difference in plain English
| Standard | What it checks | Where you configure it |
|---|---|---|
| SPF (Sender Policy Framework) | Whether a sending server is authorised by the message's SMTP envelope domain | DNS TXT record at the applicable envelope-sender domain |
| DKIM (DomainKeys Identified Mail) | Whether a message has a valid domain-associated cryptographic signature covering selected headers and content | Signing in the sending service plus a public key in DNS, usually at selector._domainkey |
| DMARC (Domain-based Message Authentication, Reporting and Conformance) | Whether a passing SPF or DKIM identity aligns with the domain in the visible From header and what policy the domain owner requests | DNS TXT record at _dmarc.domain |
An important nuance: SPF does not simply check the address printed in an email app's From field. SPF authenticates the SMTP MAIL FROM/return-path domain (with specific treatment for a null reverse-path). DKIM signs using the domain identified by the signature's d= tag. DMARC then requires at least one passing mechanism to align with the visible From domain. The definitions are set out in RFC 7208 and RFC 7489 .
2. Why a Nigerian SME should care
A business domain may send staff email through Google Workspace or Microsoft 365, customer invoices from an accounting application, receipts from a website, order alerts from an e-commerce platform and newsletters from a bulk-email provider. Those systems do not automatically inherit each other's email authentication.
A badly configured domain can lead to genuine messages being rejected, flagged as spam or failing DMARC. Meanwhile, an attacker may exploit weak domain controls to attempt direct spoofing. Authentication helps receiving systems distinguish legitimate traffic from impersonation, but a compromised authorised mailbox may still send authenticated malicious messages. Lookalike domains also remain a risk.
This is relevant to financial fraud. FlyingEze previously reported a CBN warning about fake emails and banking links . The report is useful phishing context, not evidence that any named Nigerian company has an insecure domain.
3. Step one: List every system that sends mail using your domain
Before changing DNS, identify your authorised senders. Ask the owner of each business function how it sends email, which From address it uses, and whether it supports custom DKIM signing or a custom return-path domain.
- Employee email: Google Workspace, Microsoft 365 or another mailbox provider.
- Website contact forms, password resets, booking confirmations and support messages.
- Billing, invoicing, receipts, payment reminders and customer statements.
- E-commerce order updates, shipping notices and CRM automation.
- Newsletters, promotions, events, recruitment and campaign systems.
- Servers, monitoring tools and legacy scripts that still send directly.
Record the provider, actual sending domain, required DNS records, sending volume and responsible owner. Do not confuse MX records—where incoming mail is delivered—with the SPF/DKIM/DMARC records controlling authentication of outgoing messages. It is possible to receive mail successfully while sending unauthenticated mail.
4. Step two: Create one correct SPF record
SPF is published as a DNS TXT record. There should be only one SPF policy beginning with v=spf1 at a given DNS name; multiple separate SPF policies at the same name produce a permanent error rather than a combined authorisation list.
For example, if and only if Google Workspace is the sole sender for an example domain, Google's documented record can look like this:
Host/name: @
Type: TXT
Value: v=spf1 include:_spf.google.com ~all
The include: directive authorises the provider's published sending infrastructure. ~all marks other sources as a soft failure, while -all is a stricter hard-fail statement. Neither should be selected mechanically without knowing every real sender. If your website, billing app or newsletter platform also sends email, obtain its exact SPF guidance and integrate it into the same policy where required. Some services instead rely on separate envelope subdomains or DKIM alignment.
A critical technical limit in RFC 7208 is 10 DNS-lookup-causing SPF terms during evaluation. These include nested include chains and mechanisms such as a, mx and exists. It does not mean you may safely add ten provider includes regardless of what each one expands to. Exceeding the limit results in permerror.
For domains hosted on Cloudflare, its Google Workspace DNS guide documents this example and warns against a second SPF TXT record. These are DNS records, not settings controlled by website page caching or Cloudflare's HTTP proxy.
5. Step three: Enable DKIM signing
DKIM uses a private key held by the authorised mail sender and a corresponding public key published in your DNS. The provider signs outbound messages; recipients check the signature against DNS. The private key must remain private and should never be pasted into a public DNS record.
Most providers issue a selector, such as selector1 or google, and a DNS host similar to selector1._domainkey.example.com. Some services ask for a TXT record with v=DKIM1; k=rsa; p=...; others provide CNAME records pointing to provider-managed keys. Use your actual provider's selector, record type and value—the name alone is not a working key.
For Google Workspace, its official DKIM guide describes generating the key in Admin console, publishing the provided DNS value and starting authentication. Google recommends a 2048-bit key where supported; a minimum 1024-bit DKIM key is among its sending requirements. Check the equivalent instructions if you use Microsoft 365, hosting-panel email or a transactional-mail service.
After publishing, send a real message and inspect the received authentication results. Merely placing a DNS record is insufficient if the mail service has not actually enabled signing or signs using a different domain.
6. Step four: Publish DMARC in monitoring mode
DMARC ties authentication back to the visible sender domain and publishes the domain owner's requested treatment of messages that do not pass aligned authentication. Start by checking that SPF and/or DKIM are already functioning. Google's setup guide recommends allowing 48 hours after initial SPF or DKIM configuration before enabling DMARC.
For a fictional example.com domain, a monitoring record might be:
Host/name: _dmarc
Type: TXT
Value: v=DMARC1; p=none; rua=mailto:dmarc@example.com
Here p=none requests monitoring rather than a DMARC-based reject or quarantine action; rua identifies a mailbox for aggregate reports. Create and manage that mailbox first. Reports are commonly structured XML documents, sometimes compressed; a specialist reporting service may make them easier to analyse. If reports are directed to a different domain, an additional external-destination authorisation record may be required.
The three main DMARC policy choices are:
| Policy | Requested treatment of mail that fails DMARC | Suggested use |
|---|---|---|
| p=none | No extra blocking requested by this policy | Initial monitoring and discovery |
| p=quarantine | Treat failures as suspicious, commonly spam/junk | Intermediate enforcement after legitimate senders are corrected |
| p=reject | Reject messages that fail DMARC where receivers honour the policy | Stronger protection after validating authorised mail flows |
Receiving mail services retain discretion and use additional spam and security signals. A p=none record is not an enforcement policy against direct spoofing, even though it enables useful reporting. It is a starting point, not the final security goal for many established domains.
7. Alignment: Why 'SPF pass' can still mean 'DMARC fail'
Consider a legitimate-looking message with a visible From address of billing@example.com. Suppose the sending provider authenticates its own envelope domain, mail.provider.test, and DKIM-signs with provider.test. Both mechanisms may pass their own checks yet neither domain is aligned with example.com. The message therefore fails DMARC.
Now suppose the provider signs with a valid d=example.com DKIM identity, or uses an authorised aligned envelope-sender domain. DMARC can pass if either aligned SPF or aligned DKIM passes; it does not require both to align simultaneously. In relaxed alignment, a valid subdomain and its organisational domain can align; strict alignment requires an exact domain match. The official rules are in RFC 7489 .
This makes custom DKIM signing especially valuable for services that send invoices, password resets and newsletters on your behalf. Ask each provider for domain authentication instructions instead of assuming a successful SPF lookup on an unrelated provider domain protects your brand's From address.
8. Step five: Test the real DNS and message headers
An administrator can query the public DNS records using a terminal. Replace every example hostname and selector with your own values; an empty answer may indicate DNS propagation, the wrong name, or an unpublished record.
dig +short TXT example.com
dig +short TXT selector1._domainkey.example.com
dig +short CNAME selector1._domainkey.example.com
dig +short TXT _dmarc.example.com
Check for only one v=spf1 policy at the relevant name, a matching DKIM TXT or CNAME record, and one valid DMARC policy at _dmarc. DNS consoles may automatically append the zone name: typing _dmarc.example.com into a field expecting only _dmarc can accidentally produce a doubled hostname.
Next, send test messages through each actual channel—employee mail, billing, website transactions and marketing—to external Gmail or Microsoft inboxes. In Gmail, use Show original to inspect authentication results; Microsoft 365 administrators can use message trace and header analysis. Look for spf=pass, dkim=pass and dmarc=pass, remembering that alignment is what makes the final DMARC outcome meaningful.
9. When is it safe to move to quarantine or reject?
Review DMARC aggregate reports over a representative business period, including occasional payment reminders, monthly reports and seasonal campaigns. Identify every legitimate sending source, repair SPF/DKIM configuration and verify alignment before changing a monitoring policy. There is no universal number of days that guarantees a safe switch.
A prudent sequence is to publish p=none, resolve consistent failures, consider p=quarantine, assess the effect on legitimate traffic, and only then adopt p=reject if your mail flows support it. Organisations using subdomains should also review the sp= subdomain-policy tag and any different requirements for separate mail streams.
Under p=reject, legitimate services that have not been inventoried may lose delivery. In particular, changes to website SMTP settings, finance software or marketing providers should trigger a new authentication test. Never copy a strict DNS policy from a tutorial into a revenue-critical domain without checking the current mail environment.
10. Common SPF, DKIM and DMARC failures
| Symptom | Likely cause | What to check |
|---|---|---|
| SPF permerror | Multiple SPF policies, or more than 10 lookup-causing terms | Consolidate at one name and evaluate nested includes |
| SPF fails for a billing app | Sending IP or envelope domain not authorised | Confirm provider instructions and return-path design |
| DKIM none or fail | Signing not enabled, wrong selector/key, changed message or DNS error | Check the actual DKIM-Signature and provider records |
| SPF pass, DKIM pass, DMARC fail | Neither passing domain aligns with visible From | Configure aligned DKIM or envelope sender |
| DMARC reports missing | Wrong rua mailbox, DNS typo, no reporting traffic or external-authorisation issue | Test reporting address and policy location |
| Mail stopped after p=reject | A legitimate sender was missed or a forwarding flow broke authentication | Investigate reports, headers, authorised services and rollback plan |
| Forwarded mail fails SPF | Forwarding changed the connecting server | Prefer surviving aligned DKIM and check forwarder/ARC handling |
Mail forwarding and mailing lists complicate authentication because the forwarding server may not be in the original sender's SPF policy, and modifications can break DKIM signatures. Authenticated Received Chain (ARC) can preserve authentication information through some intermediaries, but it is not a substitute for a well-configured direct sender. Microsoft's troubleshooting guide explains these failure combinations.
11. Gmail and Yahoo requirements businesses should know in 2026
Google's sender guidelines require all senders to personal Gmail accounts to authenticate with SPF or DKIM, and require senders near or above 5,000 messages per day to personal Gmail accounts to use both SPF and DKIM plus a DMARC policy. The DMARC policy may initially be p=none, but the visible From domain must align with at least one passing mechanism on directly sent messages. Google counts traffic from the same primary domain, including its subdomains.
Google also requires appropriate DNS, TLS and message formatting and expects spam rates below 0.3%. Marketing/subscribed bulk mail requires supported one-click unsubscribe and a visible unsubscribe link. These are separate requirements: adding SPF, DKIM and DMARC does not excuse a business from permission-based mailing, accurate lists or unsubscribe handling.
Yahoo's sender requirements likewise call for SPF or DKIM for ordinary senders, both plus DMARC and aligned authentication for bulk senders, and compliant unsubscribe processes. Any organisation sending commercial newsletters should review the requirements of the platforms where its recipients actually have accounts.
12. Security limits: What these records do not solve
SPF, DKIM and DMARC reduce direct use of a protected domain by unauthorised sending systems, but they are not complete email security. They cannot prevent a criminal from registering a similar-looking domain, compromising an employee's authenticated mailbox or persuading staff to send money to a fraudulent beneficiary.
They are also not a substitute for transport encryption, endpoint protection, multi-factor authentication, access reviews, invoice-verification procedures or trained staff. A DMARC-passing email can still contain malicious links. Pair domain authentication with independent verification of changed bank details and sensible identity controls. FlyingEze's guide to spotting fake recruitment messages offers another example of impersonation tactics, though it is not a DNS configuration guide.
13. Applying this to invoicing, software and publishing workflows
When an online store sends order confirmations, a hotel sends reservations, or a budgeting platform emails invoices, customers can mistake spoofed notifications for genuine messages. If a business uses P-Biz Solutions to manage operations or uses KudiScope for money tracking and planning, the operator should ensure that whatever actual email delivery service is in use has authorised domain authentication configured. Neither company's website, by itself, verifies its live SPF, DKIM or DMARC implementation.
The same principle applies to publishers sending newsletters and account notifications. Educational sites such as SuperEducational should authenticate real outbound services and avoid using a generic server identity with an unrelated visible From domain. No directly relevant verified Joynue email-security service was found, so a promotional link was unnecessary.
14. A practical implementation checklist
- List every authorised sender and the envelope, DKIM and visible From domains used by each service.
- Inspect existing SPF records; consolidate into a single valid policy per applicable name and remain within the ten-lookup evaluation limit.
- Enable provider-supported DKIM signing and publish exactly the real selectors and keys supplied by each service.
- Send sample messages to verify SPF and DKIM pass; confirm whether one passing identity aligns with the visible From domain.
- Create a controlled DMARC reporting mailbox and publish an initial
p=nonerecord at the correct DNS name. - Review real aggregate reports for recurring authorised senders, failed alignment and suspicious sources.
- Correct legitimate failures before requesting quarantine or rejection; document a rollback plan.
- After enforcement, re-test all important mail streams when providers, applications, domains or infrastructure change.
- Monitor Gmail/Yahoo sender requirements, spam rates, forwarding issues and operational incidents.
- Use multi-factor authentication and independent verification of sensitive payment instructions alongside DNS authentication.
Frequently asked questions
Do I need all three records if I send only a few business emails?
Google's baseline requirement for mail to personal Gmail accounts is SPF or DKIM, but it recommends both plus DMARC. For most businesses that control their own domain, deploying all three carefully is sensible even below bulk-sender thresholds.
Can I create two SPF records, one for Google Workspace and another for my billing provider?
No. Publish only one SPF policy at each DNS name. Combine authorised providers as appropriate, without exceeding the SPF DNS-lookup limit, or use provider-recommended domain-specific designs.
Does passing SPF automatically mean DMARC passes?
No. SPF must pass and its authenticated domain must align with the visible From domain, unless aligned DKIM independently provides the DMARC pass.
Should I set DMARC to p=reject immediately?
Not without checking the mail systems you really use. Start by monitoring and resolving authentication failures; move to enforcement when legitimate flows are consistently aligned.
Is a TXT record all I need to set up DKIM?
No. The sender must actively sign outgoing messages with its private key, and the corresponding public key must be published through the TXT or CNAME method required by the provider.
Will SPF, DKIM and DMARC guarantee my emails reach the inbox?
No. Mailbox providers also assess sender reputation, complaints, message content, user preferences and technical quality. Authentication establishes important trust signals; it does not guarantee placement.
Conclusion
A secure business email domain starts with a complete understanding of who is allowed to send mail for it. SPF authorises sending infrastructure, DKIM validates a domain-associated signature, and DMARC checks alignment with the From address while publishing a requested handling policy.
Implement them deliberately: inventory senders, publish correct SPF and DKIM records, monitor DMARC, test the messages your business actually sends and strengthen enforcement only after legitimate traffic is protected. Combined with account security and fraud-awareness procedures, this reduces avoidable spoofing risk without making unrealistic promises about deliverability.