A Nigerian business sends a customer an invoice, but instead of reaching a Gmail inbox it comes back with 550 5.7.26. Another company finds that its newsletter reaches some customers but gets a 421 4.7.32 response from Gmail. Both look like delivery failures, but they point to different problems—and the right fix depends on the full SMTP error text, not simply the word 'blocked'.
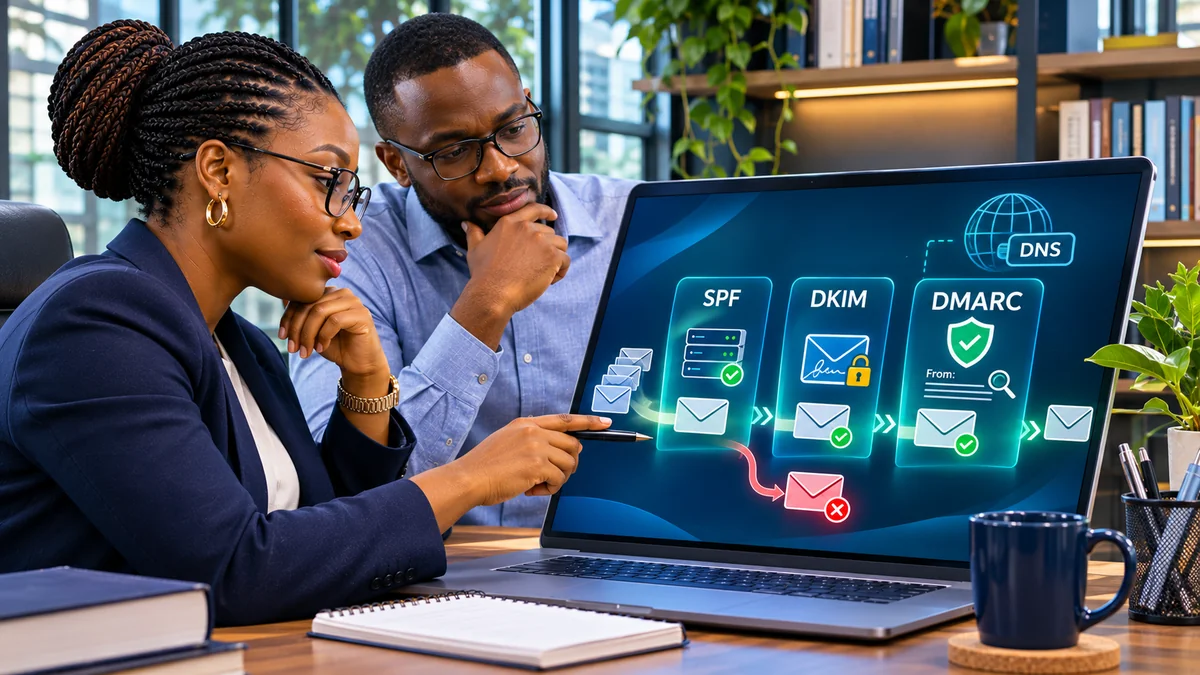
Start by reading the bounce message, identifying the service that actually transmitted the email, and testing SPF, DKIM, DMARC alignment and sending-IP DNS. Gmail's official SMTP error list identifies specific authentication, DNS, TLS and reputation failures. Google's sender guidelines also explain that personal Gmail accounts require at least SPF or DKIM authentication, with additional requirements for bulk senders.
This guide focuses on diagnosing Gmail rejection messages and repairing misconfiguration, rather than just defining the three protocols. The examples use fictional domains and simulated error snippets. Do not replace production DNS values with example records without identifying all of your legitimate mail systems. Research verified 2 November 2026.
1. First, tell a permanent rejection from a temporary delay
The first digit of the enhanced SMTP status code matters. A code beginning with 4. ordinarily indicates a transient problem: the sender's mail-transfer agent can retry after a delay. A code beginning with 5. ordinarily indicates a permanent failure for that delivery attempt. The leading SMTP response can be 421, 451, 550 or something else; read both layers and the descriptive text.
If Gmail returns 421 4.7.30, your mail server may queue and retry while you repair DKIM authentication. If it returns 550 5.7.30, it has rejected that delivery attempt; endlessly resending the same unauthenticated message will not repair it. Save the original bounce, timestamp, sending IP, recipient domain and message ID before changing anything.
Avoid treating all Gmail failures as DNS failures. 550 5.1.1 indicates a nonexistent recipient address, while 421 4.7.28 often reflects rate limiting or suspicious volume rather than a missing SPF record.
2. Gmail rejection codes: What they mean and where to start
| SMTP diagnostic | Google's documented meaning | First place to investigate |
|---|---|---|
| 550 5.7.26 | Unauthenticated sender, SPF hard-fail or a DMARC-policy rejection, depending on text | Complete authentication results and sender/DMARC policy |
| 421 4.7.27 / 550 5.7.27 | SPF failed for a bulk sender | Envelope sender and SPF policy |
| 421 4.7.30 / 550 5.7.30 | DKIM failed for a bulk sender | DKIM signing, selector and public DNS key |
| 421 4.7.32 / 550 5.7.32 | Visible From domain not aligned with SPF or DKIM domain | DMARC identifier alignment |
| 421 4.7.40 / 550 5.7.40 | Missing DMARC record or DMARC record without a policy | _dmarc TXT record and p= tag |
| 550 5.7.25 | Sending IP missing working PTR or matching forward DNS | Reverse DNS of the sending IP |
| 421 4.7.29 / 550 5.7.29 | Bulk mail not sent over TLS | SMTP transport encryption |
| 421 4.7.28 / 550 5.7.28 | Rate, reputation or unsolicited-traffic problem | Sending patterns and Google Postmaster Tools |
| 550 5.1.1 | Recipient account does not exist | Recipient address, not sender authentication |
These are descriptions of documented variants, not a rule that each code has only one underlying cause. For example, Gmail lists several different 5.7.26 texts. Copy the exact sentence and associated IP or domain into the incident ticket rather than troubleshooting from the number alone.
3. Identify the actual sender before editing DNS
A message branded as accounts@example.com might leave through Google Workspace, a Microsoft 365 tenant, a website SMTP relay, a finance application or an external bulk-mail provider. The visible From address is not necessarily the domain used for SPF.
Find the sending platform in its delivery log, the SMTP queue or the application's outbound settings. Identify the sending IP, MAIL FROM/Return-Path domain, DKIM-Signature d= domain, visible From: domain and the route that delivered the message to Gmail. For businesses operating separate billing, support and newsletter services, repeat this exercise for each one.
Do not change a company-wide SPF record to solve a problem caused by one app without checking the other apps. A careless edit could make legitimate staff mail or automated receipts fail.
4. Fix 5.7.26 and 5.7.27: Check SPF configuration
SPF tells receiving servers which infrastructure a domain authorises to send using its SMTP envelope domain. A valid SPF policy is a DNS TXT record beginning with v=spf1. Google's SPF troubleshooting instructions identify missing records, incorrect syntax, unauthorised third-party senders and lookup-limit errors as common causes.
Use this example only where Google Workspace is truly the sole system requiring SPF authorisation for the relevant domain:
Host: @
Type: TXT
Value: v=spf1 include:_spf.google.com ~all
If an invoicing provider or hosting SMTP server also sends from an envelope domain controlled by your business, confirm the provider's official requirements before adjusting the single SPF policy at that DNS name. Two separate SPF TXT policies beginning v=spf1 at one name cause an error. The SPF standard also limits DNS-lookup-causing terms to 10 during evaluation, including nested includes; exceeding the limit causes permerror.
A -all hard-fail policy can explicitly deny unlisted sending servers. Do not temporarily replace it with indiscriminate authorisation such as +all to make an error disappear. Correct the authorised provider or SMTP envelope configuration instead.
5. Fix 5.7.30: Check the DKIM signature and key
DKIM signs the outgoing message with a private key and publishes the corresponding public key under a selector-based DNS name, often selector1._domainkey.example.com. A message can fail if the sending service has not enabled signing, the DNS key is absent, its selector is wrong, or an intermediate system modifies signed content.
In Google Workspace, the administrator generates a key, publishes the supplied TXT record and then activates DKIM authentication in Admin console. Google recommends 2048-bit keys where supported. Microsoft 365 and third-party senders may provide CNAME records instead; follow your provider's actual values and do not create a made-up p= key.
Inspect the message's DKIM-Signature header for s= (selector) and d= (signing domain). Query that exact selector, and verify that the platform is actually signing with it. Microsoft's authentication troubleshooting guidance notes that mail gateways adding disclaimers or modifying messages after signing can invalidate DKIM.
6. Fix 5.7.32: SPF or DKIM passed, but the domains do not align
A business can have working SPF and DKIM yet still fail DMARC. Consider a fictional invoice whose visible From is billing@example.com while SPF authenticates relay.vendor.test and DKIM signs vendor.test. The two checks may pass on their own, but neither is aligned with the domain visible to the customer.
DMARC requires at least one passing aligned mechanism: SPF with an aligned envelope domain, or DKIM with an aligned signing domain. For direct mail to personal Gmail accounts, bulk senders must configure both SPF and DKIM but only one of these needs to align. Google explains this in its sender FAQ .
Ask the provider to configure custom-domain DKIM signing or an aligned custom return-path, where supported. Under relaxed alignment, a subdomain can align with its organisational domain; strict alignment requires an exact match. Do not rewrite the From header to a domain that your organisation does not own simply to satisfy a test.
7. Fix 5.7.40: Check whether DMARC exists and is valid
DMARC is published at _dmarc.example.com as a TXT record. Gmail's 4.7.40 and 5.7.40 variants indicate that a bulk sender lacks an appropriate DMARC record or the record does not specify a policy. An initial example for a fictional domain is:
Host: _dmarc
Type: TXT
Value: v=DMARC1; p=none; rua=mailto:dmarc@example.com
The p=none value is a valid monitoring policy that can satisfy Gmail's basic bulk-sender DMARC-policy requirement; it does not request rejection of spoofed mail. Establish the reporting mailbox before publishing rua. If reports go to an external domain, authorisation may be required there. Google's DMARC setup guidance recommends allowing SPF and/or DKIM to operate first and observing results before stronger enforcement.
Do not change a working p=reject policy to p=none simply to conceal an authentication problem. First inspect legitimate mail flows, check alignment and decide on a controlled remediation. The receiving service can also reject suspicious messages under its own security rules regardless of a DMARC policy.
8. Check public DNS with terminal commands
Run DNS queries from a terminal. Replace example.com, the selector and the sample IP with the real values from your message headers and provider. A command succeeding does not prove the corresponding mail service is configured correctly.
dig +short TXT example.com
dig +short TXT _dmarc.example.com
dig +short TXT selector1._domainkey.example.com
dig +short CNAME selector1._domainkey.example.com
dig +short -x 203.0.113.25
The first command can reveal an SPF TXT record at the root, but you must query the actual envelope domain if it differs from the visible From domain. The next commands inspect DMARC and DKIM; the last checks reverse DNS for an example IP. The documentation-reserved IP 203.0.113.25 is not a real business mail server.
Check whether your DNS dashboard expects the relative hostname _dmarc or the full hostname. Entering the full domain into a field that automatically appends the zone can accidentally publish _dmarc.example.com.example.com. Changes may take time to appear across resolvers because of caching and propagation.
9. Fix 5.7.25: Reverse DNS and sending-IP identity
A 550 5.7.25 rejection indicates the sending IP lacks a suitable PTR record or the forward DNS for its hostname does not resolve back to that IP. This is distinct from SPF, which uses sender authorisation; both can matter for direct SMTP delivery.
Run a reverse lookup for the real sending IP, then a forward A/AAAA lookup for the returned hostname. For example, the provider might configure mail.example.com as PTR for its IP and ensure the hostname resolves back to that IP. The reverse zone is usually managed by the IP-address owner or hosting provider—not automatically by changing an A record in Cloudflare.
If your website sends directly from a virtual private server, ask its hosting provider whether it supports custom reverse DNS, outbound port access and suitable mail reputation. If it does not, use an established authenticated SMTP relay instead of attempting to bypass Gmail's requirements.
10. Fix 5.7.29: Enable TLS, then check 4.7.28 reputation warnings
Google requires TLS for senders to personal Gmail accounts and documents 5.7.29 for bulk email delivered without TLS. Check that the sending mail-transfer agent negotiates STARTTLS or another supported secure transport method with its upstream SMTP host. This is not fixed by simply enabling HTTPS on your website.
By contrast, 4.7.28 often signals unusual sending volume, spam complaints or rate limits. Google's Postmaster Tools can show authentication, spam rate, domain/IP reputation and delivery errors where sufficient traffic exists. Google says senders should keep reported spam rates below 0.3%; a lower target is preferable. Stop unrequested campaigns, audit list sources and avoid dramatic traffic spikes.
A domain can have perfect SPF, DKIM and DMARC but still be blocked because of complaints, suspicious links, malformed messages or poor reputation. Do not promise that fixing DNS will guarantee inbox placement.
11. Read headers from a successfully delivered test message
If some messages arrive, send a controlled test from each legitimate mail channel to a Gmail account. In Gmail, open the message and choose Show original. Look at the Authentication-Results header. A fictional successful example may look like this:
Authentication-Results: mx.google.com; spf=pass smtp.mailfrom=bounce.example.com; dkim=pass header.d=example.com; dmarc=pass header.from=example.comThis example passes DMARC because header.d=example.com aligns with header.from=example.com. The SPF-authenticated bounce.example.com can also align under relaxed settings. A real header may include other checks and more complex results; Gmail's display and each provider's logs are the source of truth for that test.
For a message Gmail rejected before accepting, there may be no recipient-side message header to examine. Use the sending provider's SMTP log, original payload metadata and bounce/NDR response instead. Do not ask an employee to forward a bounce containing unnecessary personal data to a public forum.
12. Special cases: Forwarding, mailing lists and app servers
Forwarding can break SPF because the forwarding IP was not authorised by the original sender's envelope domain. If a forwarder modifies the message body or signed headers, DKIM can also fail. Authenticated Received Chain (ARC) may help some intermediaries preserve prior authentication context, but it is not a replacement for correct direct-sender authentication.
For a Laravel, WordPress or other application, distinguish the server's local sendmail path from authenticated SMTP or a transactional-email API. Confirm configured sender identity, credentials, provider-authorised DKIM, bounce address and retry handling. An app's 'sent' status may mean only that it queued a message or received acceptance from an SMTP relay—not that Gmail delivered it.
Production systems should keep a unique message or business-event identifier, record provider delivery status and apply rate-limited retries only where appropriate. Reusing the same billing event without idempotency can produce duplicate invoice or payment-reminder emails when a queue worker retries after an ambiguous failure.
13. A safe repair sequence for a Nigerian business
- Preserve evidence: Save the full bounce, enhanced SMTP code, sending IP, timestamp, service and message ID.
- Classify: Separate temporary 4xx deferrals, permanent 5xx failures and recipient-address mistakes.
- Identify the sender: Map the From, Return-Path, DKIM domain and provider for each failing channel.
- Check DNS: Verify SPF uniqueness and lookup count, real DKIM selector, valid DMARC policy and sending-IP PTR.
- Fix the specific failure: Authorise legitimate infrastructure, activate aligned signing or repair TLS/reverse DNS.
- Test safely: Send low-volume sample mail to Gmail and inspect provider logs and accepted-message headers.
- Monitor: Review DMARC aggregate reports, Postmaster Tools and actual application outcomes before changing enforcement.
- Retire bad workarounds: Do not use open SPF policies, fabricated DKIM records, purchased 'whitelisting' or repeated high-volume resending.
When multiple services share one domain, coordinate changes with finance, customer support, marketing and the website administrator. A correction for the newsletter must not silently break booking confirmations or payroll notices.
14. When to escalate, and what to send your provider
If the provider claims all records are correct but Gmail continues rejecting messages, open a support request containing the exact SMTP response, sending IP, visible From, Return-Path, DKIM selector, sample timestamp, recipient domain, redacted header or message ID, DNS results and the outcome of a controlled retry. Ask the provider to verify actual outbound signing, envelope sender identity, TLS negotiation and reverse-DNS ownership.
If you manage Google Workspace, check the Admin console's email logs and DKIM settings; for Microsoft 365, use message trace and the provider's authentication tools. Gmail Postmaster Tools specifically covers traffic to personal @gmail.com and @googlemail.com addresses and may show little or no data for low-volume domains. It is not a universal dashboard for all Google Workspace recipients.
15. What this means for Nigerian payment and hospitality platforms
Restaurants, hotels and online merchants may send bookings, receipts, password resets and invoices through different services. Organisations evaluating P-Biz Solutions or KudiScope should verify the email authentication of the actual sending provider behind any chosen integration; a product catalogue or feature page is not proof that a specific custom domain is configured correctly.
Publishers and educational platforms such as SuperEducational have the same responsibility when sending newsletters or account notices. No verified Joynue service directly related to Gmail DNS troubleshooting was identified, so a promotional link was not included. FlyingEze's coverage of phishing emails targeting bank customers explains the broader impersonation risk; its cybersecurity portfolio guide offers related learning ideas, not a substitute for Google's delivery requirements.
Frequently asked questions
What does Gmail error 550 5.7.26 mean?
It can indicate unauthenticated mail, an SPF hard-fail or rejection under a domain's DMARC policy. Read the full diagnostic sentence because the same enhanced code covers different variants.
Why does DMARC fail when SPF and DKIM pass?
Passing results may authenticate domains unrelated to the visible From domain. DMARC needs at least one passing aligned SPF or DKIM identity.
Should I add two SPF records for my office and website?
No. Each relevant DNS hostname should have only one SPF policy. Combine legitimate authorisations carefully or use your provider's recommended envelope subdomains.
Can I fix Gmail delivery by changing MX records?
MX records control inbound message routing. They are not normally the cure for outgoing SPF, DKIM, DMARC or sending-IP PTR failures.
Does p=none mean my business has no DMARC?
No. It is a valid monitoring policy, though it does not request DMARC-based quarantine or rejection. Use aggregate reports before moving to stronger enforcement.
Will authentication guarantee emails reach Gmail inboxes?
No. Google also evaluates reputation, spam complaints, secure transport, message formatting and other safety signals. Authentication is necessary for reliable sending but not a delivery guarantee.
Conclusion
When Gmail rejects business email, the fastest safe approach is to identify the exact SMTP failure rather than blindly adding more DNS records. The code can point to SPF, DKIM, DMARC alignment, missing policy, reverse DNS, TLS, reputation or a nonexistent recipient—and each requires a different response.
Preserve the bounce, identify the actual sending service, verify public DNS, inspect message headers and test small batches after a targeted fix. For Nigerian businesses relying on email for invoices, bookings and customer communication, this disciplined workflow protects legitimate delivery while reducing the risk of domain spoofing and avoidable outages.