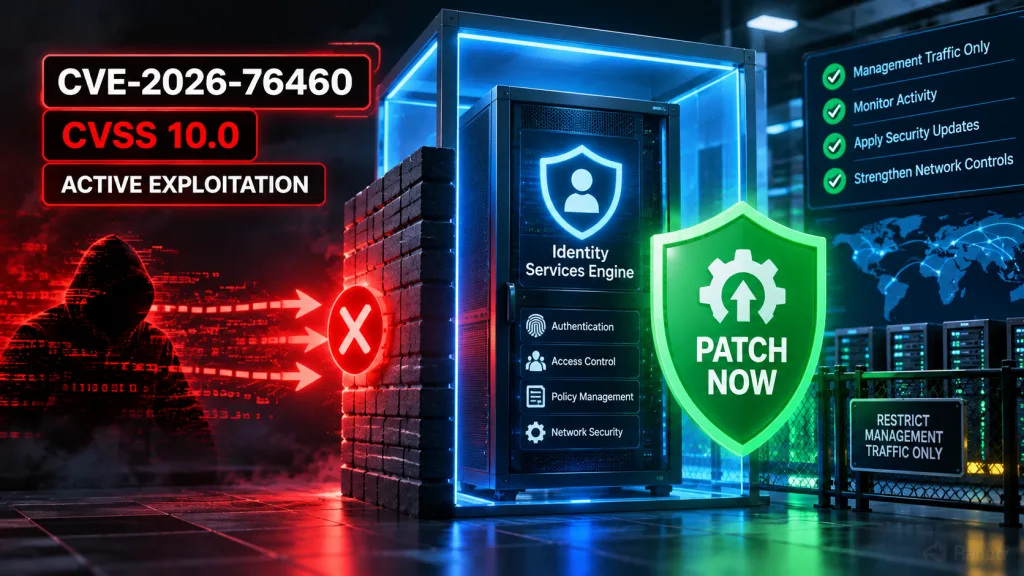
Organisations running Cisco Identity Services Engine should urgently check their exposure to CVE-2026-76460, a maximum-severity authentication-bypass vulnerability that Cisco says is being actively exploited.
The flaw affects Cisco ISE and ISE Passive Identity Connector. Because the vendor reports active attacks and no workaround, patching or upgrading to a fixed release should be treated as an immediate operational priority.
What CVE-2026-76460 is
CVE-2026-76460 is an authentication-bypass vulnerability in Cisco’s identity-services platform. Public reporting on Cisco’s advisory says the issue carries a CVSS score of 10.0 and can be exploited without authentication. Successful exploitation can give an attacker highly privileged control, including the ability to execute commands as root.
ISE is often a central component of enterprise network-access policy. That makes a compromise especially serious because identity and access infrastructure can influence which users and devices are trusted across a network.
Active exploitation changes the priority
A vulnerability known to be exploited in the wild should generally move ahead of similarly severe flaws for which exploitation remains theoretical. Defenders have less room to wait for a normal maintenance cycle when attackers are already using a weakness.
Administrators should use Cisco’s current security advisory as the authoritative source for affected and fixed software versions. Product version and deployment details matter, so organisations should not assume that a generic package update covers every node.
There is no workaround
Cisco says there is no workaround for the vulnerability. That makes moving to a fixed release the primary remediation rather than relying on a configuration change as a substitute.
While preparing the update, defenders can still reduce risk by tightly restricting access to management interfaces, allowing only necessary administration networks and reviewing firewall or access-control rules for unintended exposure. Those measures reduce attack surface but should not be treated as replacements for the vendor fix.
What defenders should check
First, inventory all ISE and ISE-PIC nodes and record their exact software releases. Compare those versions with Cisco’s advisory and identify every node requiring remediation.
Second, review relevant logs for unexpected API activity, authentication anomalies, unfamiliar administrative changes, suspicious commands or outbound connections. An organisation that finds evidence of compromise should follow its incident-response process rather than assuming patching alone removes an attacker’s persistence.
Third, protect credentials and secrets accessible to affected systems. If investigation indicates unauthorised privileged access, credential rotation and a broader assessment of connected systems may be necessary.
Patch the whole deployment deliberately
Identity infrastructure is often deployed as multiple coordinated nodes. Teams should plan upgrades according to Cisco’s supported sequence, verify service health after each change and ensure that no forgotten or secondary node remains on a vulnerable build.
After remediation, confirm the installed version independently and continue monitoring. An emergency patch is complete only when the organisation can demonstrate that all affected assets have moved to a fixed state.
Bottom line
CVE-2026-76460 combines the factors defenders least want to see: maximum severity, unauthenticated access, privileged impact, active exploitation and no workaround. Organisations using Cisco ISE or ISE-PIC should verify their versions against the vendor advisory and move affected systems to fixed releases without unnecessary delay.