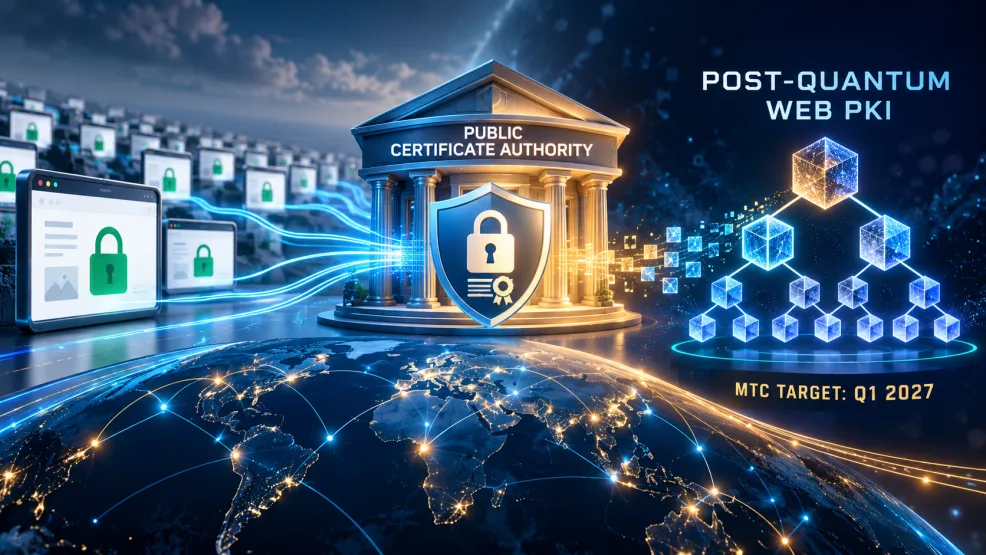
Cloudflare has announced its intention to become a public certificate authority, moving from one of the web's largest consumers of publicly trusted TLS certificates toward issuing certificates itself.
The company says it has applied for inclusion in the Chrome, Apple, Microsoft and Mozilla root programmes and signed a definitive agreement to acquire an established trusted root from GlobalSign.
Why Cloudflare wants to become a CA
Certificate authorities sit at the centre of the Web Public Key Infrastructure, issuing certificates browsers use to authenticate websites. Cloudflare says operating its own public CA would give it more direct control over certificate issuance at internet scale.
The post-quantum problem
Cloudflare is also preparing for a future in which conventional public-key cryptography must be replaced or supplemented by post-quantum algorithms. Simply placing large post-quantum signatures into today's certificate model can create substantial performance overhead.
What are Merkle Tree Certificates?
Cloudflare is working on Merkle Tree Certificates, which use compact proofs tied to a larger authenticated tree rather than carrying all authentication material in the same way as a conventional certificate. The approach is intended to make post-quantum authentication more practical at web scale.
Availability is not immediate
Cloudflare's announcement is an intent to operate a public CA, not a claim that every browser already trusts certificates it issues. Classical public issuance depends on acceptance into browser and operating-system root programmes. Cloudflare is targeting production Merkle Tree Certificate issuance for the first quarter of 2027.
What website operators should do now
There is no need to replace existing TLS certificates simply because of this announcement. Website operators should continue following their certificate provider's guidance and track browser and standards-body timelines for post-quantum migration.
Bottom line
Cloudflare's CA plan is important because it connects certificate issuance, browser trust and post-quantum migration in one programme. The technical direction is clear, but general availability still depends on root-program approvals and future rollout milestones.