AI governance programmes can look mature on paper and still fail in practice if the organisation has not built the culture required to govern data well.
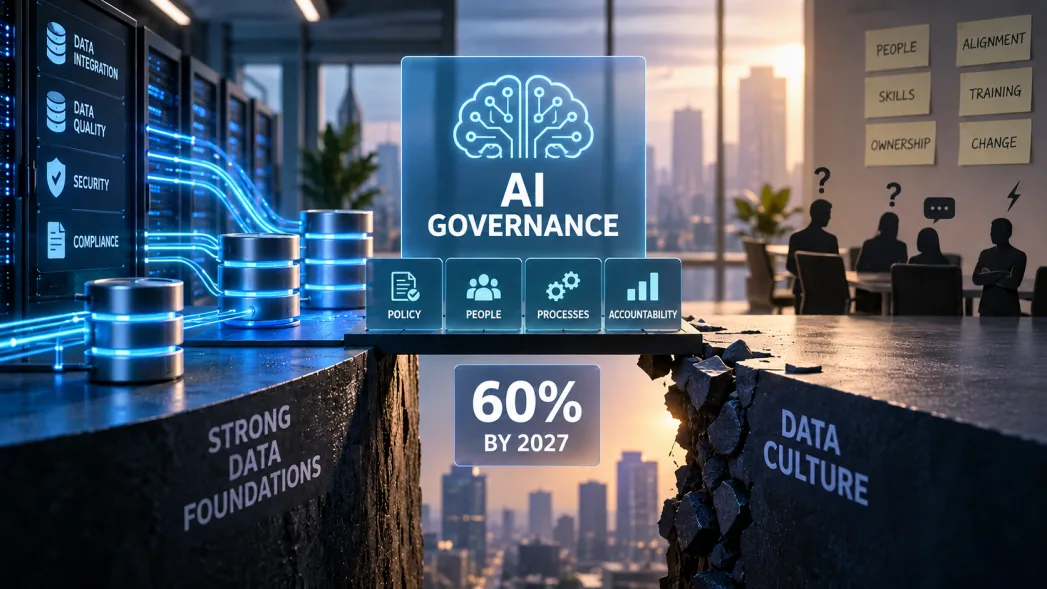
That is the central warning in new Gartner research published on 21 September 2026. The research firm predicts that by 2027, 60% of organisations that fail to address cultural challenges around data governance will be unable to govern artificial intelligence successfully.
The prediction is significant because many AI-governance programmes are being built around technical controls: model inventories, security reviews, access policies, data quality checks and compliance frameworks. Those controls matter, but they do not automatically solve questions of ownership, accountability, incentives and day-to-day behaviour.
What Gartner’s prediction is really saying
Gartner’s point is not that data governance technology is unimportant. It is that organisations also need what the firm describes as AI-ready stakeholders, not only AI-ready data.
An organisation may have clean datasets, access controls and formal policies, yet still struggle if teams do not agree on who owns the data, who can approve AI use, when an exception is allowed, who is accountable for a model’s output, or how business teams should respond when governance slows a project down.
Those are cultural and operating-model questions rather than database questions.
Why strong data foundations are not enough
Good AI governance depends on the quality, provenance and permitted use of the data behind a system. But even strong technical foundations can break down when people work around controls, ownership is unclear or governance is treated as a compliance exercise rather than part of normal product and business decision-making.
For example, a company can maintain a detailed data catalogue but still allow teams to reuse sensitive information for AI training without a clear approval path. It can implement model monitoring but fail to assign someone responsibility for acting on the alerts. It can write an AI policy but leave employees uncertain about which tools are approved for customer or confidential data.
In each case, the technical layer exists, but the organisational layer is weak.
The five cultural issues that often undermine AI governance
1. Unclear ownership
AI governance becomes difficult when no one knows who has final responsibility for the data, the model, the business process and the resulting decision. Organisations should define accountable owners at each layer rather than assuming the technology team owns every AI risk.
2. Governance that arrives too late
If legal, security, privacy and data-governance reviews appear only at the end of a project, teams may see them as blockers. Bringing those stakeholders into design and procurement earlier reduces the chance that controls become emergency fixes.
3. Incentives that reward speed but not stewardship
Teams are more likely to bypass governance when success is measured only by shipping quickly or increasing automation. Governance works better when data quality, documentation, responsible use and remediation are part of performance expectations.
4. Policies that employees cannot apply
A policy that says “use AI responsibly” is not enough. Teams need practical examples: which data can be uploaded, which tools are approved, when human review is mandatory, how incidents are reported and who can grant an exception.
5. Weak feedback loops
Governance cannot remain static while AI systems, regulations and business uses change. Organisations need a way for employees to report friction, near misses, policy gaps and emerging risks so controls can improve without waiting for a major incident.
What AI-ready stakeholders look like
AI-ready stakeholders understand enough about data and AI risk to make decisions within their role. A product manager does not need to become a machine-learning engineer, but should understand when training data raises privacy concerns. A data owner should know which downstream AI uses are permitted. Security teams should understand how model access and connected tools change the attack surface.
The goal is distributed competence with clear accountability.
A practical governance model
Organisations can strengthen the cultural side of AI governance with a small number of concrete operating practices.
- Assign named owners: identify who owns data, models, business outcomes and risk acceptance.
- Use simple decision gates: define which AI use cases require privacy, security, legal or executive approval.
- Train by role: give developers, data teams, marketers, HR staff and executives guidance relevant to the decisions they actually make.
- Keep evidence: document data sources, intended use, approvals, testing and important model changes.
- Monitor behaviour as well as models: measure repeated policy exceptions, shadow-AI use, unresolved ownership and ignored alerts.
- Review governance regularly: update controls as tools, regulations and business risks change.
Culture does not replace technical controls
There is a risk of overcorrecting and treating culture as a substitute for technical governance. It is not. Access controls, data lineage, security testing, privacy safeguards, model monitoring and auditability remain necessary.
The stronger approach is to connect the two. Technical controls make governance enforceable; culture makes people use and maintain those controls correctly.
Why this matters now
AI adoption is moving from experiments into customer service, software development, analytics, marketing, operations and decision support. As those systems gain access to sensitive data and business processes, governance failures become harder to isolate.
Organisations therefore need to ask more than whether their data is ready for AI. They also need to ask whether their people, incentives, responsibilities and decision processes are ready to govern it.
Bottom line
Gartner’s 60% prediction is a forecast, not a measured outcome. But the underlying lesson is practical: AI governance is unlikely to succeed when data governance exists only as policy documents and technology controls.
Companies that want durable AI governance should build clear ownership, role-specific skills, usable policies, accountable decision paths and feedback loops alongside the technical data foundation. AI-ready data is necessary. AI-ready organisations are what make it governable.