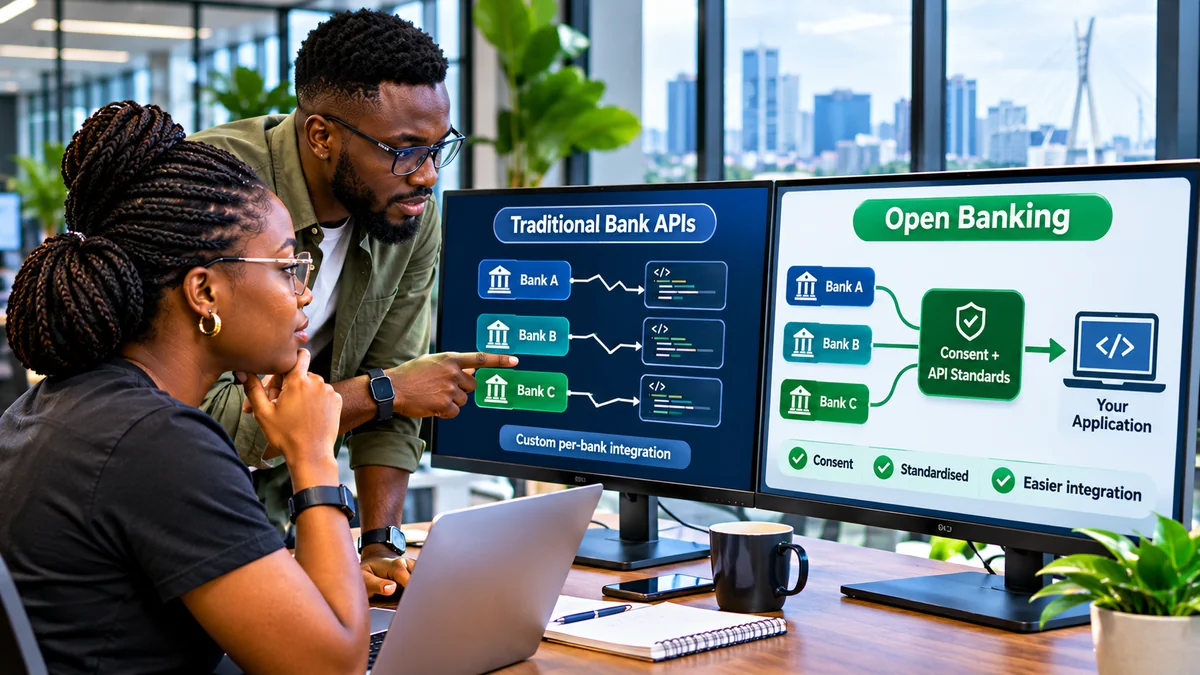
For Nigerian fintech developers, the biggest difference between open banking and traditional bank integrations is not simply the API format. Traditional integrations connect a product to a particular bank, processor or partner under that provider's own commercial and technical rules; regulated open banking is intended to make permissioned access to financial data and services more consistent across participating institutions. In practice, a common standard can reduce duplicated engineering work, but it does not automatically remove onboarding, regulatory checks or the need to test every provider.
A fintech connecting to three banks today may need three onboarding processes, three sets of credentials, different transaction fields and distinct error-handling rules. A standardised approach could make cross-bank account information and consent more predictable. Yet the two models can coexist: a payment gateway, an interbank payment rail and a consent-based account-data API solve different problems.
The Central Bank of Nigeria (CBN) issued its Regulatory Framework for Open Banking in 2021 and Operational Guidelines on 7 March 2023 . The framework defines participant roles, consent, security and oversight. But developers should not confuse having a regulatory framework with having a universally available production service. An Open Banking Nigeria update from July 2026 says the planned 1 August 2025 nationwide launch did not occur, while the CBN's Fintech Report published in 2026 identifies fragmented APIs and inconsistent data-sharing standards as persistent problems.
This guide explains the two architectures, their trade-offs and what an engineering team should build now. Research verified 3 November 2026.
What counts as a traditional bank integration?
A traditional integration is a bilateral or provider-specific connection. A bank may give an approved business an API for account enquiries, corporate payouts or collections. A payment processor may provide virtual account collections, card acceptance and webhook notifications. Another financial institution may use file uploads, host-to-host messaging or proprietary reporting formats.
Such integrations are often valuable and already operational. They may support a company's current business better than waiting for a broader open-banking ecosystem. The challenge is heterogeneity: connection methods, credentials, documentation, identifiers, payout schedules, rate limits and error responses differ.
Consider a startup building a dashboard for merchants with accounts at three institutions. One connection might return balances in minor currency units, another in decimal naira strings, and a third only through downloadable statements. One may use a transaction reference that is stable across requests, while another exposes different references for settlement and the original payment. Developers must normalise these differences rather than pretending the APIs are interchangeable.
What makes an integration “open banking”?
Under the CBN guidelines, an API Provider (AP) makes permitted data or services available, an API Consumer (AC) uses them, and the customer controls permission to access relevant information. The framework also envisages a participant registry and requirements for security, operational risk, customer experience and data protection.
The intended improvement is not that financial information becomes public. It is that the authorised access process has a common regulatory and technical foundation. The Open Banking Nigeria API Standard v1 illustrates account-data, consent, OAuth-style token and idempotency concepts, but it explicitly describes its specifications as a draft with mock endpoints and dummy values. It is not a live transaction service or proof that any named bank already implements every example.
Actual implementation must follow the authorised bank or provider's currently supported specification and applicable CBN requirements—not blindly copy a prototype's sample credentials or routes.
Open banking versus traditional integrations: side-by-side
| Dimension | Traditional bank or provider API | Regulated open banking model |
|---|---|---|
| Technical contract | Often proprietary to each partner | Designed around common participant and API standards |
| Customer permission | Varies by service and governing law | Explicit, scope-specific and time-bound consent required |
| Onboarding | Individual commercial, security and technical approval | Regulated participation plus applicable institutional onboarding |
| Authentication | Provider-specific keys, signatures, tokens or other controls | Framework includes secure token/consent controls; actual implementation must be verified |
| Coverage | Depends on contracted partners | Depends on participating institutions and live rollout |
| Transaction data | Different schemas and references | Greater consistency is the intended goal, not a present guarantee |
| Payments | Can support collections, transfers and payouts where authorised | Data access and payment initiation are distinct permissions and capabilities |
| Main engineering risk | Maintaining many incompatible adapters | Assuming standards or consent flows are universally live |
Neither approach should be labelled categorically cheaper, faster or more secure. Security depends on implementation, and total cost depends on real API availability, commercial terms, testing, compliance and operational support.
1. Design a provider adapter rather than hard-coding bank differences
Whether using existing integrations or future open-banking connections, build an internal interface that separates your application from the bank. For example, an AccountConnection component may represent the authorised institution, account, available scopes and token status; a TransactionImporter converts provider records to a common data format; and a ReconciliationEngine matches those records against invoices.
Use the same internal contract for all providers, but retain raw source identifiers and original payloads where permitted for auditability. A common record can include institution ID, account ID, source transaction ID, booking date, value date, direction, amount in the smallest currency unit, currency, narration and retrieval time.
Do not invent a transaction ID if the bank did not provide one. Where unique identifiers are missing or unstable, document a cautious composite-key deduplication strategy and send collisions to review. Never treat a matching amount alone as proof that a customer has paid.
2. Separate account-data access from moving money
Fetching an account balance or transaction history is not the same as initiating a debit, accepting a card payment or sending an interbank transfer. Read-only access should be designed with narrower permissions and lower risk than a service authorised to move funds.
For context, NIBSS's NIP service guide describes interbank functions such as name enquiry, direct credit, direct debit, balance enquiry and transaction-status query. Those are payment-system capabilities available through relevant institutional arrangements; they are not automatically an open-banking account-data API that any app may call.
Likewise, a gateway such as Paystack provides merchant-specific payment verification. Its Verify Payments documentation requires checking the underlying transaction status and reference. A payment gateway and an open-banking data connection can complement each other, but neither is an automatic replacement for the other.
3. Build consent as part of the product, not a hidden checkbox
Consent management is a major architectural distinction. The CBN's 2023 guidelines require customers to know the type and purpose of information requested and provide explicit, time-bound consent with a means to withdraw access. They include verification of consent and token-based controls, and provide for a record of permission changes.
In a fintech onboarding flow, show the institution involved, specific accounts or data classes, reason for the request, access frequency, expiry and withdrawal route. Request only what the product needs. A cash-flow dashboard may need transaction history and balances; it does not follow that it needs broad payment-initiation authority.
Store permission status with timestamps and approved scopes, handle token expiry, and stop new collection when access has expired or been revoked. Do not assume that deleting a UI connection revokes the provider-side permission: verify the provider's actual revocation process. Audit how already-collected data is retained or deleted in accordance with applicable legal requirements.
The Nigeria Data Protection Commission explains duties under the Nigeria Data Protection Act, 2023, including lawful and accountable processing and data-subject rights. Consent to connect a bank account does not authorise unrelated profiling or marketing uses.
4. Plan authentication and security around real risks
Traditional bank APIs may use IP allowlists, mutual TLS, OAuth access tokens, HMAC signatures or other arrangements. Open Banking Nigeria's draft describes bearer tokens, OAuth-related consent flows and idempotency headers, but that draft should not be treated as a production security configuration.
In either model, keep secrets and refresh tokens on secured servers, encrypt sensitive records, rotate compromised credentials, enforce least-privilege access and separate development from live environments. Validate signed callbacks before processing them and monitor failed authorisation attempts. Never log full passwords, OTPs, private keys or unrestricted customer financial data.
For example, Paystack's webhook guide documents validation of the x-paystack-signature using HMAC-SHA512. That rule applies to Paystack webhooks specifically; a different bank or open-banking participant may require a different signature method. Follow the live provider's documentation rather than reusing another provider's algorithm.
5. Use idempotency, retries and reconciliation deliberately
Networks fail. An API may accept a request but lose the response before your service receives it. An event can be delivered twice, or an import process can restart halfway through a batch. Retrying blindly can double-create ledger entries or repeat payment instructions.
Use request idempotency keys where supported, unique constraints on source events, durable queues, backoff for recoverable errors and a record of the last confirmed import cursor. Treat 401 as an authorisation issue, 429 as a rate-limit signal where documented, and provider timeouts as uncertain outcomes that may require a status check—not proof that an operation failed.
For money movement, a retry should use the provider's documented idempotent mechanism and query the original transaction status first. For read-only imports, make ingestion repeatable without duplicating transactions. A ledger should preserve what was originally recorded and use explicit adjustments rather than silently rewriting history.
The draft Open Banking Nigeria standard includes idempotency principles, but real-world behaviour, key lifetime and error handling must be confirmed for each production provider.
6. Understand what “one integration for many banks” really means
A common standard aims to reduce bespoke development, but it does not abolish commercial relationships, institution availability, onboarding checks, consent or compatibility testing. Banks may join at different stages, support different authorised scopes or have different uptime characteristics.
The CBN's Fintech Report explicitly identifies fragmented APIs and inconsistent data-sharing protocols as ongoing concerns. As of 3 November 2026, public evidence reviewed does not establish that every Nigerian bank offers the same operational open-banking endpoints.
When evaluating an aggregator, request a bank-by-bank coverage matrix showing supported account types, transaction history depth, refresh frequency, outage handling, pricing, consent expiry and production availability. A mock sandbox connection and a bank-approved live connection are different things.
Architecture example: a Nigerian SME finance application
Consider a fictional fintech building a dashboard for restaurants and retailers. Its initial product matches invoices to bank credits, combines account balances and helps business owners forecast near-term cash needs.
The architecture should have a connection layer for banks and payment providers, a normalisation and consent layer, an immutable transaction ledger, a matching service, and a dashboard and exception queue.
| Stage | Developer responsibility |
|---|---|
| Connect | Validate approved provider credentials, accounts and consent scopes |
| Import | Retrieve authorised records, log source and freshness, handle paging and retries |
| Normalise | Convert amounts, timestamps, currency and references without losing provenance |
| Match | Compare transactions with invoices; route ambiguous matches for review |
| Reconcile | Separate direct bank credits, gateway charges, processing fees and net settlements |
| Report | Display verified balances, unmatched items, last sync and forecast assumptions |
Suppose a gateway confirms ₦500,000 of customer charges and charges ₦10,000 in fees. If a ₦490,000 payout arrives at the bank later, the system must clear the gateway settlement receivable rather than count the payout as an additional ₦490,000 of revenue. The same rule applies whether the bank record is obtained from a traditional export or an authorised API feed.
This is an illustrative architecture, not evidence that a particular bank or platform supports all the capabilities described.
Should developers choose direct integrations, aggregators or wait?
Direct integration makes sense when a product needs a known provider's live function, the company can meet onboarding requirements and the use case is narrow. It can give greater control, but each additional provider increases support and maintenance work.
An aggregation partner may reduce engineering effort by handling multiple bank-specific connections. Evaluate its authorisations, upstream dependencies, fees, continuity plans, security and the consistency of its normalised data. A single vendor can still become a point of failure.
Standards-aware architecture is sensible when the product expects future multi-bank connectivity. Design reusable adapters and a consent model now, but do not announce a live nationwide open-banking feature until the relevant connections are validated.
The recommendation is usually hybrid: ship with available, authorised integrations and maintain a modular design that can support compliant open-banking connections when they are demonstrably available.
Cost and performance measures that matter
Measure total cost of ownership, not just per-call API prices. Include onboarding, security testing, engineering maintenance, incident response, data storage, provider support and consent-related customer support. Compare integration uptime, successful authorised connections, fresh transaction coverage, reconciliation match rates, exception volumes and time to recover after outages.
Do not invent nationwide API pricing or claim that standardisation automatically reduces costs by a fixed percentage. Financial return depends on actual bank coverage, transaction volume, staff time saved and business outcomes. A small single-bank product may find a direct integration sufficient; a finance platform serving many institutions may benefit more from standardisation.
A developer's production-readiness checklist
- Define whether the product needs account information, payment acceptance, payment initiation or some combination.
- Confirm the legal role, partner authorisations and actual bank/provider coverage rather than relying on marketing diagrams.
- Document purpose-specific permission, scopes, expiry, revocation and customer support paths.
- Build source-specific adapters and normalise data without losing original transaction references.
- Secure API credentials, protect customer data and authenticate callbacks using each provider's official scheme.
- Implement idempotent jobs, durable event processing, safe retries and incident monitoring.
- Test duplicate events, stale data, partial outages, reversed payments and failed consent renewal.
- Keep transaction verification, accounting reconciliation and customer-facing payment status separate.
- Obtain legal and privacy review before using sensitive account data for scoring or unrelated analytics.
- Launch narrowly with human-reviewed exceptions and expand only when production evidence supports it.
For broader retail operations, a business system can be valuable even before open banking is widely interoperable. FlyingEze has examined organised digital collections through FCMB Collect , while P-Biz Solutions lists business-management products. Confirm specific current payment and bank-integration capabilities with any provider; neither reference is proof of universal open-banking connectivity.
Frequently asked questions
Does open banking mean every Nigerian bank uses one API today?
No. The CBN framework and industry draft standards exist, but public evidence reviewed in November 2026 does not establish universal live bank adoption. Verify each institution's actual production support.
Is a bank's API automatically an open-banking API?
No. A bilateral corporate API or payment-gateway endpoint may be proprietary and governed by different commercial arrangements. Regulated open banking adds a specific framework for participants, permission and security.
Can developers use the Open Banking Nigeria example URLs for live payments?
No. The published specification labels its API examples as draft and mock data. Use actual institution-approved production endpoints and credentials only after authorised onboarding.
Does open banking replace NIBSS Instant Payment?
No. Interbank payment rails and consent-based data-sharing arrangements serve different functions, although products may use both under the correct authorisations.
Should a fintech collect users' online banking passwords?
A secure permissioned integration should follow authorised authentication flows rather than asking users to hand over unrestricted credentials. Apply CBN security rules and Nigerian data-protection requirements.
Can a product support both traditional APIs and future open banking?
Yes. A modular provider-adapter architecture can maintain existing live integrations while making room for standardised ones. The internal ledger and reconciliation controls should not depend on a single provider's format.
Conclusion
Open banking aims to make authorised financial connectivity more reusable, but Nigerian fintech developers still need dependable production integrations, strong consent controls and careful reconciliation. Traditional bank APIs remain useful for specific services. A standardised future may reduce fragmentation, provided participating institutions implement compatible, secure and operational connections.
The practical strategy is to build modularly, verify the current bank-by-bank reality, separate account data from payment movement and preserve auditability. That will make a fintech product more resilient today—and better positioned for broader open banking adoption when it becomes verifiably available.