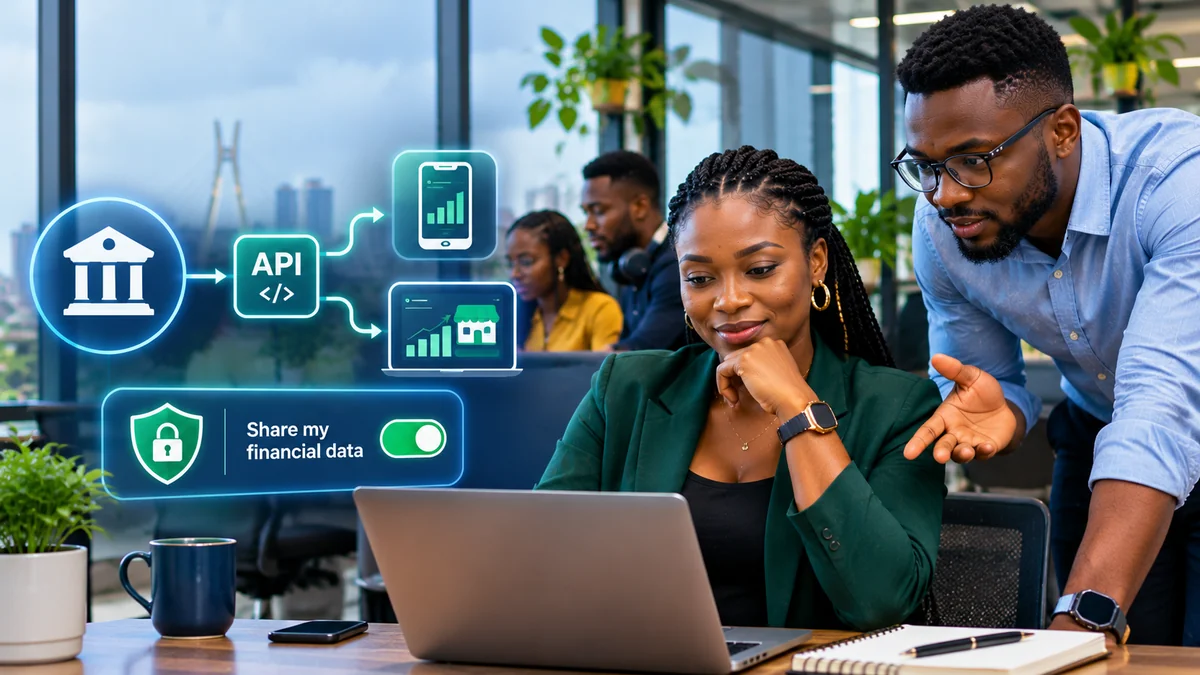
Open banking in Nigeria is a regulated approach to sharing financial information and accessing certain banking services through secure application programming interfaces (APIs), with the customer's permission. In practice, a customer could authorise a budgeting app, lender or other approved participant to obtain specified account information without handing over an online-banking password. The customer should know who is requesting the data, why it is needed, how long access lasts and how to revoke it.
The Central Bank of Nigeria (CBN) established the regulatory framework in 2021 and issued operational guidelines on 7 March 2023 . The promise is improved competition, easier account aggregation, more informed credit decisions and new financial products. But regulation is not the same as a fully operational nationwide network. The expected August 2025 launch did not occur, and the official and industry sources checked for 3 November 2026 did not establish a new confirmed nationwide go-live date.
This guide explains the model, what consent should mean, how APIs and the registry fit together, which opportunities Nigerian businesses can explore, and the security and privacy limitations that remain.
What does open banking mean for a Nigerian customer?
Think of the difference between handing an app your bank password and giving it narrowly defined permission to receive information through a secured connection. Open banking is designed around the second approach. A bank or another eligible API provider makes permitted data or functionality available, an API consumer requests it for a specific service, and the customer grants the necessary authorisation.
For example, a person with accounts at two banks might want to see spending across both in a personal-finance dashboard. With a suitable open banking arrangement, they could approve access to transaction information for a limited time. The app could then classify spending and help identify recurring bills without asking the person to upload new screenshots every month.
That is an illustrative use case, not a claim that every Nigerian bank currently supports the same live consent-based APIs. Availability depends on actual participation, approved interfaces, system readiness and any service-specific rules.
Why Nigeria introduced open banking rules
Nigerian banks and fintechs already exchange information through different technical integrations, but individually negotiated connections can be inconsistent and expensive to maintain. The CBN's 2023 guidelines aim to establish clearer participant responsibilities, security standards and more consistent access to financial services.
Its fintech policy report published in 2026 records industry concerns about fragmented APIs, identity verification, account aggregation and inconsistent service standards. This reinforces an important distinction: Nigeria has a regulatory policy for open banking, but implementation and interoperability remain works in progress.
The value of common rules is not that any application can read any bank account. It is that properly authorised participants could develop compatible services with more predictable technical, consent and risk-management requirements.
How open banking works: three roles and one permission
The CBN's operational guidelines identify three essential roles.
| Role | What it does | Example |
|---|---|---|
| Customer | Decides whether the data or service access is authorised | A bank account holder approving a defined request |
| API Provider (AP) | Makes permitted data or functionality accessible through an API | A participating bank or another eligible data provider |
| API Consumer (AC) | Requests the permitted information or service for an approved purpose | An eligible budgeting, lending or accounting service |
A simplified account-linking journey would look like this:
- A customer selects a bank and chooses to link an account inside an eligible financial application.
- The application explains the data it wants, the purpose, frequency and expiry of access.
- The customer approves or declines the request through an appropriate authenticated process.
- The API provider verifies the authorisation and sends only the permitted information to the API consumer.
- The application uses the data for the agreed service and keeps appropriate records.
- When consent expires or is withdrawn, future access under that permission should stop, subject to applicable system and legal requirements.
This is a conceptual example of the intended architecture. Real implementations will have additional validation, security, eligibility and error-handling stages.
What customer consent must include under CBN rules
Customer consent is not supposed to be a vague button buried in a long privacy policy. The 2023 CBN guidelines require consent to be explicit and time-bound. A customer must be able to accept or decline, understand the requested information and purpose, and withdraw permission.
Before authorisation, the API consumer should disclose its legal and brand identity, relevant registry identification, the type of data or account access requested, the duration and frequency of access, and how withdrawal works. The guidelines call for authentication, recorded permission changes and mechanisms for immediate revocation.
| Consent question | What a clear request should tell the customer |
|---|---|
| Who wants access? | The identifiable organisation requesting permission |
| What information? | Specified account details, balances or transaction records, where permitted |
| Why? | For example, consolidating spending or supporting an affordability assessment |
| How often? | A one-time retrieval or periodic access, as applicable |
| For how long? | A clear expiry or agreed period, not indefinite access |
| How do I stop it? | An understandable way to view and revoke authorisation |
The CBN's customer-experience appendix also provides for consent revalidation annually and/or after 180 days of inactivity, according to its wording. A customer should not have to surrender an online-banking password to an unknown third-party representative merely to give consent.
Does revoking consent delete everything already shared?
No—not automatically. Revocation is primarily a way to stop future access under the permission. Information already lawfully processed may be subject to data-retention requirements, legal obligations, rights of deletion or other restrictions. The Nigeria Data Protection Act 2023 explains that withdrawal does not retrospectively make previous lawful processing unlawful.
Customers should therefore read the retention notice and ask the service what happens to information already obtained. For businesses, the correct design is to distinguish consent revocation, access-token invalidation, data retention and erasure requests rather than promise that they are all the same action.
What are open banking APIs, and how are they secured?
An application programming interface (API) is a structured way for one system to request information or a service from another. An open banking API could provide permitted account information or support an authorised payment-related workflow, depending on the applicable service category and participants.
The CBN's technical standards describe HTTPS, OAuth 2.0, REST-style interfaces, JSON and ISO 20022 messaging, tokens, access controls, signing, encryption, rate limits and audit measures. These standards are intended to reduce the risks of uncontrolled credential sharing and inconsistent integrations.
For a developer, two concepts matter particularly:
- Scope: Permission to read specified transactions should not silently become permission to initiate transfers or retrieve unrelated personal information.
- Expiry and revocation: Access tokens and stored consent records need to reflect the customer's current, authorised permissions. Expired or withdrawn permission should not keep working.
Open banking does not make fraud impossible. Poor app security, phishing, malicious consent screens, leaked tokens and excessive data retention can still harm customers. Providers and consumers must implement effective monitoring, incident response and security controls.
What is the Open Banking Registry?
The CBN guidelines establish an Open Banking Registry (OBR) to support oversight and transparency about participating organisations and the APIs within the ecosystem. The 2023 document says the CBN will provide and maintain it, with records of registered participants and their business-registration identifiers.
Industry implementation materials published by Open Banking Nigeria describe a model in which NIBSS would operationalise registry and central consent-management infrastructure. These are important developments, but documentation about planned infrastructure must not be mistaken for proof that every bank has completed onboarding or that every consumer can use a nationwide service today.
The registry's purpose is to help establish who participates in the formal ecosystem. It does not mean any company displaying “open banking” on its website is automatically licensed for lending, payment initiation or other separately regulated activities.
Is open banking live across Nigeria in 2026?
A universal nationwide go-live could not be independently confirmed as of 3 November 2026. The CBN issued its framework in 2021 and its operational guidelines in 2023. An industry target for August 2025 was missed. In October 2025, a CBN official told TechCabal that the national system had not yet gone live. Open Banking Nigeria's July 2026 update continued to describe regulatory preparations and an awaited directive, while the CBN's fintech report documented continuing gaps.
Some Nigerian fintechs already have their own bank integrations and financial-data products. Those commercial connections are not evidence that the entire CBN-standardised open banking regime has launched nationwide.
A separate development occurred in 2026: the CBN's second Regulatory Sandbox cohort included a Data-Enabled Financial Services track for solutions involving permission-based data sharing, account aggregation, payment initiation and credit analytics. Sandbox testing is not the same as a nationwide production rollout, and admission does not grant an unrestricted licence. The August 2026 application announcement should not be interpreted as proof that applications remain open indefinitely.
Before publishing a launch claim or promising a product integration, check current CBN circulars, participant notices and official onboarding arrangements.
Business opportunities created by open banking
Open banking offers possible opportunities far beyond digital lenders. Here are practical uses Nigerian businesses and developers can evaluate when secure, compliant connections are available.
1. Personal budgeting and financial dashboards
A financial-planning tool could consolidate authorised transactions from several banks, classify expenses, show recurring commitments and help a user compare actual spending with a monthly budget. Customers benefit from fewer manual imports, but the application must be transparent about data access, retention and the accuracy of its categories.
For example, a personal or workspace money-tracking app could use permitted account data to improve reconciliation. That is a potential architecture, not a claim that any named budgeting product currently offers a CBN-standard open banking connection.
2. Faster accounting and bank reconciliation for SMEs
Businesses often spend time matching deposits to invoices, customers and orders. A suitably authorised integration could retrieve transaction records and suggest matches to outstanding invoices. Staff would still need controls for duplicate payments, refunds, incorrect references and exceptions.
This matters for shops, hotels, restaurants and service providers managing multiple branches or accounts. Any implementation should maintain the business's approved account ownership, staff permissions and accounting audit trail.
3. More informed lending and affordability checks
With appropriate customer permission, a lender could assess income patterns or cash-flow stability without relying solely on screenshots of statements. That may improve verification and reduce document handling, but it cannot guarantee approval, a cheaper loan or a fair automated decision.
Providers must evaluate credit risk carefully, avoid discriminatory or misleading conclusions and explain significant automated outcomes where required by data-protection law. A transaction-history connection alone is not a lending licence.
4. Payment services and embedded finance
Open banking standards contemplate authorised payment-related workflows as well as data exchange. In the right regulated arrangement, an application may support a customer-approved payment action without storing banking passwords. The real availability of payment initiation depends on the services and approvals in place; it is not safe to assume that every Nigerian bank supports this today.
Developers should use appropriate confirmation, transaction identifiers, idempotency and reconciliation procedures. A pending request or successful API response must not automatically be treated as irrevocable receipt of money.
5. Fraud detection and customer verification
Financial institutions might combine permitted transaction insights with other lawful risk signals to identify inconsistencies and unusual activity. But more data is not automatically better security. A system must limit collection to legitimate purposes, secure the records and avoid exposing sensitive account details to unnecessary parties.
FlyingEze has previously covered Nigerian banks' concerns about payment-data localisation , a related reminder that data location, controls and regulator expectations matter to financial infrastructure.
Opportunities for Nigerian fintech startups: a readiness checklist
Before building a product around a promised national open banking connection, a startup should establish which business model is lawful and commercially feasible.
- Define the user problem. Is the product solving manual reconciliation, poor cash-flow visibility, onboarding delays or a specific lending problem?
- Identify required data and permissions. Use only information necessary for the described service; separate read-only access from payment capabilities.
- Check the regulatory perimeter. Determine whether the business needs authorisation, a regulated partner or another licence. Sandbox participation is not a general licence.
- Verify live technical availability. Confirm the actual API provider, environment, commercial terms and onboarding process rather than rely solely on marketing announcements.
- Design consent management first. Include plain-language requests, access scopes, expiry, revocation, evidence logs and secure customer authentication.
- Protect data end to end. Establish encryption, secret management, least-privilege access, logging, breach response, retention and deletion procedures.
- Test failure cases. Account disconnection, API outages, consent expiry, duplicated events and mismatched transactions must be handled without corrupting records.
- Measure user benefit. Track reconciliation accuracy, time saved, support complaints and customer trust rather than assuming API connectivity alone creates value.
Startups processing personal information should also read FlyingEze's published guide on assessing Nigerian business registration obligations with the NDPC . Open banking participation does not displace Nigeria's broader data-protection requirements.
How safe is open banking for customers?
It is potentially safer than informal password sharing when implemented according to the CBN's authentication, access-control and consent standards. But security depends on actual controls and participant behaviour, not the label “open banking”.
Customers should be wary when an app demands their bank login password in a chat, asks them to send OTP codes to an agent, makes an unexplained request for years of transaction history, or provides no way to identify the requesting company. Always check the institution's genuine interface and understand what is being authorised.
Businesses should remember that the Nigeria Data Protection Commission supervises the Nigeria Data Protection Act's rules on lawful, secure and accountable personal-data processing. Consent must be specific and informed where required, while other lawful bases may apply to different processing activities. Under the CBN's open banking arrangement, customer permission remains a foundational requirement for the covered data-sharing access.
Open banking versus ordinary bank transfers, bank APIs and screen scraping
| Method | What it means | Important distinction |
|---|---|---|
| Normal bank transfer | Customer sends money using bank or wallet payment services | Does not automatically give a third party ongoing access to account data |
| Private bank API integration | Two organisations connect through individually agreed technical interfaces | May exist without national open banking standardisation |
| CBN-standard open banking | Defined participants exchange permitted data or services under shared rules | Requires appropriate participation, consent, security and operational readiness |
| Screen scraping / credential sharing | A tool reads an account through captured screens or reused login details | May create greater security and compliance risks; not equivalent to a properly authorised API flow |
The CBN's 2023 security appendix specifically warns participants against screen-scraping-type practices inimical to the ecosystem. Safer integrations should avoid encouraging customers to disclose full banking credentials to unrelated applications.
Frequently asked questions
Does open banking mean anyone can see my bank balance?
No. The regulated model requires eligible participants, customer permission and defined access controls. A public announcement of open banking is not permission for arbitrary organisations to inspect private accounts.
Can I withdraw consent after connecting an app?
The CBN guidelines provide for consent to be time-bound and revocable. Revoking access should stop future access under the permission; previously processed records may still be subject to lawful retention and data-protection obligations.
Is open banking the same as mobile banking?
No. Mobile banking is a way to use financial services through a phone. Open banking concerns controlled data or service connections between eligible organisations, using APIs and customer authorisation.
Can fintech startups build open banking products without a banking licence?
The answer depends on the activity, role, required accreditation and applicable regulations. Not every API consumer is necessarily a deposit-taking bank, but a startup cannot provide regulated financial services merely by calling itself an open banking platform.
Has Nigeria's national open banking system fully launched?
A confirmed nationwide go-live was not independently established from the sources reviewed by 3 November 2026. The rules exist and the CBN has supported relevant sandbox testing, but the two should not be confused with verified universal production availability.
Will open banking automatically make loans cheaper or approvals faster?
No. Better-permissioned data may help suitable lenders make more informed assessments, but outcomes depend on lending rules, data quality, business models, credit risk and responsible decision-making.
Conclusion: Customer control is the opportunity—and the responsibility
Open banking in Nigeria offers a pathway to financial services that connect through consent-based APIs rather than fragmented manual processes. The 2021 framework and 2023 operational guidelines describe customer choice, participant responsibilities, secure technical standards and regulatory oversight. For businesses, potential benefits include improved financial dashboards, accounting reconciliation, better credit assessment and appropriately regulated payment services.
The critical 2026 qualification is implementation: the national rules exist, but a nationwide go-live and universal connectivity were not confirmed in this review. Consumers should evaluate real consent requests carefully, while developers should verify current CBN and provider readiness before promising features.
The organisations that ultimately benefit most will be those that solve a genuine customer problem while making privacy, security, revocation and operational reliability part of the product from the start.